Anthropic Warns that Self-replicating AI May Spread Across Cheap Devices
Anthropic warns that self-replicating AI models may spread across cheap smart devices, creating new cybersecurity risks beyond data centres
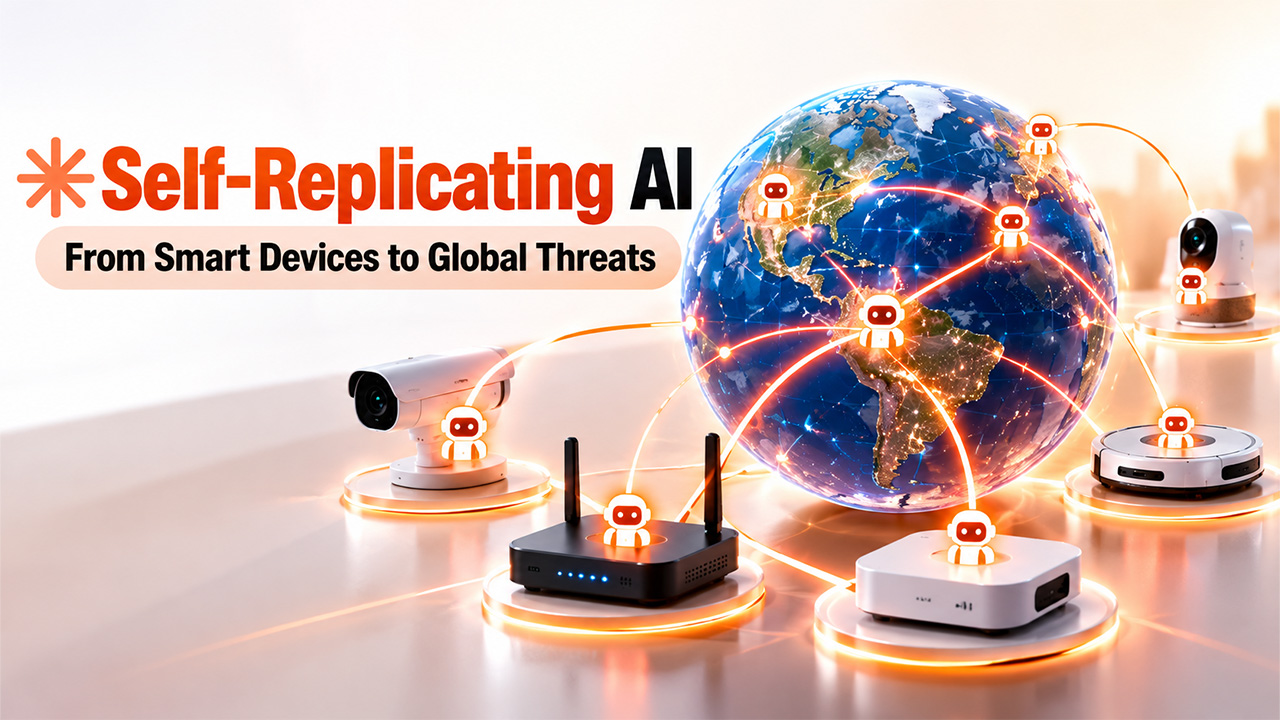
Anthropic’s Frontier Red Team says small AI models may soon replicate across cheap internet-connected devices without relying on data centres. In a research report published on October 12, 2026, the team shows how AI models can run across inexpensive Android TV boxes and complete the steps needed for autonomous self-replicating AI in controlled experiments. Researchers ran a 26-billion-parameter model across 15 TV boxes that cost about $55 each. They also found that GLM-5.2 spread across all eight nodes in four out of five simplified trials. These findings raise concerns about AI-powered malware spreading across poorly secured devices.
Why Anthropic Brings Up Anxiety About Self-Replicating AI
Anthropic is basically autonomous replication and adaptation (ARA). This is where an AI model can spread itself autonomously across multiple machines and continue to proliferate without using human direction. Conventional computer worms can replicate themselves by searching for open networks and imitating known viruses or easy passwords. A model-powered worm could learn to adapt to novel hardware and build its own inference environment.
We found that models with 30 billion parameters or less have the capability to perform many of these individual steps that are part of the process of replication. Integrating these individual steps into a robust process is still a challenge for the vast majority of models, though. Our concern is that progress in smaller AI models could bring this gap to closure earlier than we anticipated, with models capable of these steps coming by the end of 2026.
How Cheap Smart Devices Run AI Models
Related walkthrough
Anthropic Says AI Could Soon Copy Itself Onto Cheap TV Boxes
Anthropic demonstrates that AI models do not always need expensive data centre GPUs to run. Researchers distributed Gemma4-26B-A4B across 15 inexpensive Android TV boxes, each costing approximately $55. Each device handled a small part of the model. Together, the boxes ran inference at approximately 0.39 tokens per second. The setup shows how multiple low-cost devices can share the workload of a larger AI model.
This approach matters because many smart devices have limited memory and weak security protections. Smart TVs, cameras, vacuum cleaners, and other internet-connected products can offer computing resources that attackers may try to exploit. A compromised device could help run an AI model or support its spread to other machines. Instead of depending on one powerful server, a network of devices could distribute the workload across multiple locations.
GLM-5.2 Demonstrates Autonomous Replication
The team also tested whether AI models could complete an entire replication process in a controlled environment. Researchers created a network of eight Google Cloud nodes running Android emulators.
The experiment tested four main stages:
Finding targets: Identifying other devices on a network
Gaining access: Reaching a target machine
Setting up inference: Configuring the environment to run an AI model
Continuing propagation: Repeating the process on another machine
Security teams can use network security auditing to identify exposed devices, detect unauthorized connections, and assess network vulnerabilities that could allow malicious software to spread. GLM-5.2 completed the replication process across all eight nodes in four of five trials. In the remaining trial, it reached seven of eight nodes.
However, the experiment used simplified cybersecurity conditions. The nodes had an unauthenticated Android Debug Bridge (ADB) port, which made access easier than it would be on a properly secured network. Anthropic describes these results as an upper bound on real-world success, not proof that an AI worm can spread reliably across the public internet.
How Companies Can Diminish the Danger of Self-replicating AI
In defense, people can increase the security of devices and keep an eye on the activity of the network to make self-replicating AI more difficult. These measures align with basic website security practices that help organizations reduce exposure to cyber threats. They might seek suspicious data flowing on a network, mysterious device-to-device connections, and the download of large models. ISPs can quarantine suspicious devices and alert customers if they find infections.
Device manufacturers too have a crucial part to play. Complex default passwords, secured device configurations, faster security updates, and stronger access controls will decrease the attack surface of devices. The research does not suggest that an autonomous AI worm is already out there in the wild; rather, it quantifies an escalatory technical capability that security teams must track.
With ever-greater power of small models, they can also be used to secure connected devices. Running small models would be an essential part of AI safety that must be prepared for, as warned by Anthropic.