SSIS 469: Quick Troubleshooting and Prevention Guide
Fix SSIS 469 error caused by authentication failures, permission issues, or locked configurations with SQL permissions, security context, and package settings.
If you work with SSIS long enough, error 469 eventually shows up, usually right after you thought a package was ready to go. It’s a security-related error, and while the message itself can look cryptic, the root cause almost always traces back to permissions, authentication, or a locked package configuration.
Understanding exactly where the problem actually exists is the difference between spending 5 minutes and a few hours troubleshooting. Once you have the actual layer at fault identified, whether it is security context, Kerberos delegation, or package protection, fixing the error becomes relatively easy.
In this blog, we’ll walk through what SSIS 469 actually is, why it happens, and how to resolve it without derailing your production ETL pipelines.
What Is SSIS 469?
SSIS 469 is a security-related error that occurs if there is an attempt made by a package to do something which the underlying system is not allowing it to do. This is usually in the form of something like “The user does not have permission” or “Cannot access the database under the present security context”. Even though it may seem like a very obvious problem with access rights, there may be different layers, protection levels in the package, security roles in SQL Server, or even Windows accounts being used for the jobs involved. Understanding database permissions is also important when troubleshooting access-related database errors.
This error is more important than one might think. If this error stops the package in its tracks, then the data flow coming into your reports and dashboards will stop completely. Being able to determine the exact location from which this permission problem comes is key.
Why Does SSIS 469 Error Occur?
A few recurring issues are almost always behind this error:
Mismatched security contexts:
The most common cause by far. If the login executing the package doesn’t have the right database permissions, SSIS blocks the action outright. Windows authentication errors show up the same way when a targeted file or folder is restricted to a different service account.
Kerberos double-hop failures:
These tend to appear without warning. When credentials fail to delegate properly across servers, the SSIS runtime can’t authenticate to remote data stores, most often on scheduled jobs or when the SSIS server sits separately from the database engine.
Locked package configurations:
Package protection settings can quietly cause this too. If a package is set to EncryptSensitiveWithUserKey, a different user or service account won’t be able to decrypt the connection strings, which triggers a 469 error immediately.
Isolating which of these three is actually responsible authentication, permissions, or package settings narrows your troubleshooting scope considerably.
What Is SSIS 469 Error?
SSIS Error 469 generally surfaces when an integration package attempts to implement an action that is not allowed in the underlying system. The message often appears as “The user does not have permission” or “Cannot access the database under the present security context.” Though it looks like a straightforward permission issue, it can also be tied to how data interacts with SQL Server or even a MySQL Database Schema during migration. This means the problem may involve multiple layers: SSIS package configurations, SQL Server security, and Windows user accounts.
The error is quite significant because the movement of data must be smooth for reports and analytics. When SSIS 469 errors show up, it stops a complete workflow, delaying important insights. Recognizing where the permission breakdown happens, whether on the destination, data source, or within SSIS itself, facilitates quick resolutions later on.
Common Causes of SSIS 469 Error
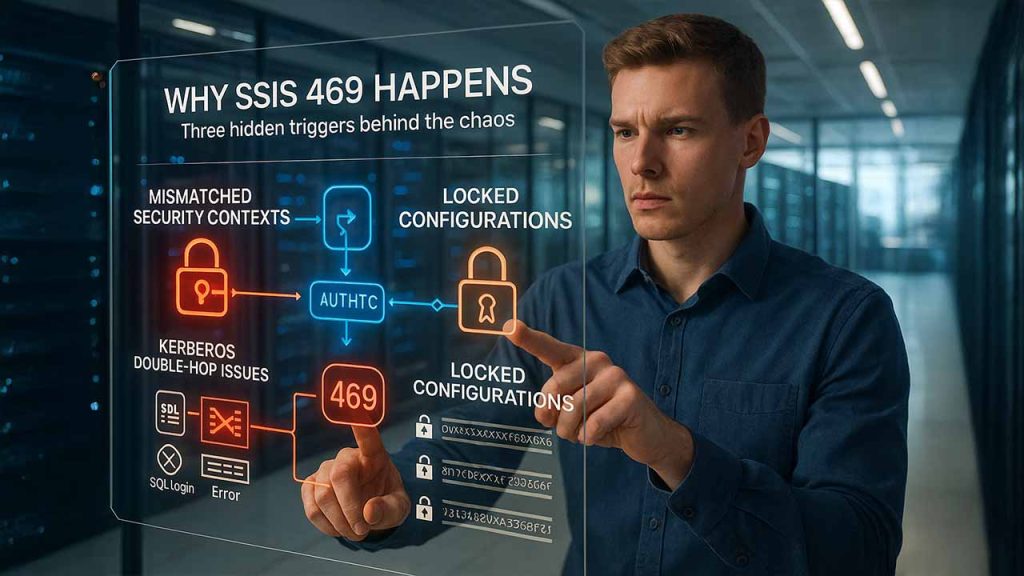
Numerous factors cause SSIS Error 469, as explained in detail in the following points:
- Mismatched Security Contexts: It is one of the most common factors. The server login executing the package does not have effective database rights; SSIS blocks access. Similarly, users can use Windows authentication errors if the targeted file or folder resource is limited to another service account.
- Double-hop Issues in Kerberos Setup: Such issues can show up without any problem. When credentials do not delegate across the servers properly, the SSIS runtime cannot authenticate to remote data stores. Users generally face these issues on the scheduled jobs or when servers operate on a server that is different from the database engine.
- Locked Configuration Details: Third, package protection can sometimes lock configuration details. If you set the SSIS package to EncryptSensitiveWithUserKey, another service or user will not decrypt connection strings. This directly leads to an access failure flagged as a 469 error.
If you isolate each cause, such as authentication delegation, security rights, and package settings, you can effectively reduce troubleshooting scope.
Learn:
How to Fix SSIS 469 Error
To efficiently diagnose SSIS 469, implement the following steps:
- Review the Error Message: You can begin by reviewing the error message frequently. Generally, it ensures particular information related to where failure has occurred. This can make your investigation more data-driven.
- Check Event Logs: In the next step, you must assess your event logs as well as execution reports in SQL Server Management Studio (SSMS). Such tools provide in-depth insights into the execution of packages, enabling you to highlight issues related to the flow of data or transformations.
- Make Full Use of Breakpoints Within Your SSIS Packages: In development, when you pause and check data at numerous stages, this technique aids in recognizing discrepancies before they grow into major errors such as SSIS 469.
SSIS 469: Detailed Troubleshooting Guide
Related walkthrough
Robots Are Learning to Work Like Humans

When SSIS 469 happens, you can implement the below steps to diagnose as well as resolve the problem:
- Check protection at the package level: Open visual studio SSIS or SSMS package and give confirmation to the protection level. If it is based on user key, you can modify it with Encrypt Sensitive with Password or Don’t Save Sensitive.
- Verify Your SQL Permissions: Sign in using the exact SQL proxy or service account your job runs under, not your own credentials. Confirm that the account holds CONNECT rights on the target database, along with SELECT and INSERT permissions on the relevant schema.
- Review File Access of Windows: If your package writes or reads a flat file, make sure that the service account can write, read, and list directory contents. OS-level file ACLs generally cause permission denial unexpectedly.
- Inspect Double Hop Setup: For remote resources, leverage the klist tool to confirm Kerberos tickets. If your delegation fails, establish constrained delegation in Active Directory or leverage SQL authentication in the connection string.
- Recover Package Configurations: If a package that previously ran fine suddenly fails, check for a missing or corrupted .dtsconfig or .json file. Use a recovery tool to extract the original configuration before rerunning the package.
Implementing such steps generally exposes the main reason behind SSIS error 469. After implementing the issue, interactively implement the package and on the server to make sure it completes without any problems.
Best Practices of Prevention
Avoiding SSIS 469 begins with powerful developmental guidelines:
- Unified Mechanism Across Environments: You need to adopt a single mechanism of protection across various environments. EncryptSensitiveWithPassword is a safe option because you can easily share passwords in DevOps pipelines without aligning it with the profile of the users.
- Utilize Database Role: Leverage database roles instead of individual user grants. Create a specialized SSIS_Role in your database and provide only the required rights. Then, proxy to this role or map your service account. This approach streamlines future audits and minimizes risks of misconfiguration.
- Have Clear Documentation on the Authentication Strategy: Irrespective of whether you leverage Kerberos delegation, managed service accounts, or SQL authentication, ensure a clear runbook. This can ensure that administrators or new members can check settings without any guesswork.
- Test Package Deployments: Check the effectiveness by testing package deployments in a staging environment where the real-time production environment can be created. In this way, you can identify the permission gaps early in the testing process by implementing nightly test jobs. This helps you recognize problematic scenarios right in your sandbox, not in the ETL pipeline.
Logging and Tracking
Consistent tracking recognizes SSIS issues before they can derail the production reporting:
- SSIS Catalog Logging: Begin by allowing SSIS catalog logging. Detect all the OnWarning and OnError to an SQL table. Assessing such logs provides instant insights into why and where 469 errors happen.
- Enterprise Tracking Solutions: You can also incorporate enterprise tracking solutions. Numerous teams utilize managed infrastructure solutions that connect to SIEM tools. They provide alerts on why real-time SSIS tasks fail because of authentication or permission problems.
Once integration issues are resolved, workflow automation can help businesses reduce manual handoffs and keep information moving consistently between teams and systems. - Email Notifications for Prevalent 469 Issues: Establish email notifications for common 469 errors. If you encounter the same error three times in one hour, you can use the notifications to notify your teams in real time. This helps you avoid unnoticed failure from causing missed SLAs and stale dashboards.
- Weekly Review of SSIS Execution History: Assess the execution history of SSIS errors on a weekly basis. Especially pay attention to spikes in job failures. Early detection of patterns associated with SSIS 469 saves a high amount of time that goes into firefighting in busy production windows.
Comparison of Error Codes
It is important to understand how SSIS 469 adjusts to other prevalent errors. The following table performs a quick comparison between common SSIS errors:
| Error Code | Main Cause | Main Fix |
|---|---|---|
| SSIS 469 | Security or Permission Context | Modify rights and protection level |
| SSIS OxC020E8 | Invalid mapping of columns | Match destination/source schema |
| SSIS Ox80131500 | Script task null reference | Initialize objects or include null checks |
If you segment your errors in this way, you can identify patterns much more quickly. SSIS 469 stands apart because of its associations with security. While different errors often indicate data structures or scripting logins, 469 makes you check logins, review accounts, and package protection.
The above table can serve as a quick reference when you are juggling numerous SSIS problems. It accelerates root cause analysis and makes sure that you apply the best fix without any guesswork.
Conclusion
Facing the SSIS error 469 can be a little daunting. However, it follows a clear discovery path: recognize the broken security setup, implement the appropriate settings or rights, and ensure the outcome. By following a structured way of troubleshooting and implementing preventive practices, you can vastly minimize the chances of facing this error in production, just as systematic diagnosis helps resolve network-level issues like DNS_PROBE_FINISHED_NXDOMAIN.
Incorporating automated alerts and centralized logging allows you to keep ahead of problems. Ensure that you remain current and test deployments in an environment that emulates production. In this way, SSIS 469 remains a known checkpoint instead of an unexpected failure.
Ultimately, a steady focus on authentication, permissions, and package design converts SSIS 469 from a problem to a learning point. Using this guide as a reference, you can easily resolve this problem and ensure that your ETL pipelines run without any problems.
FAQs for SSIS 469
Why Does SSIS 469 Occur?
It happens when an SSIS package attempts an action the system won’t authorize, most often tied to mismatched security contexts, Kerberos delegation failures, or a package protection level that blocks decryption for the account running it.
Can SQL Server Permissions Cause SSIS 469?
Yes, and it’s actually one of the most frequent causes. If the SQL login or service account executing the package lacks the right CONNECT, SELECT, or INSERT permissions on the target database, SSIS blocks the action and surfaces it as error 469.
Does SSIS Package Protection Level Affect SSIS 469?
It does. A protection level like EncryptSensitiveWithUserKey ties sensitive data to the specific user who created the package. When a different account tries to run it, that account can’t decrypt the connection strings, which triggers the error.
How Can I Check SSIS 469 Errors in SSISDB?
Query the catalog.executions and catalog.event_messages views inside the SSISDB catalog database. These log detailed execution history and error messages, including the exact step and package where the permission failure occurred.
Can SQL Server Agent Cause SSIS 469 Errors?
Yes, if the job step runs under a proxy or service account that doesn’t have the same permissions as the account used during development or manual testing. This mismatch is a common, easy-to-overlook cause of 469 errors, specifically on scheduled jobs.